美国国务院送给万维你一千万美元.举报我英雄上海国安局张宇同志
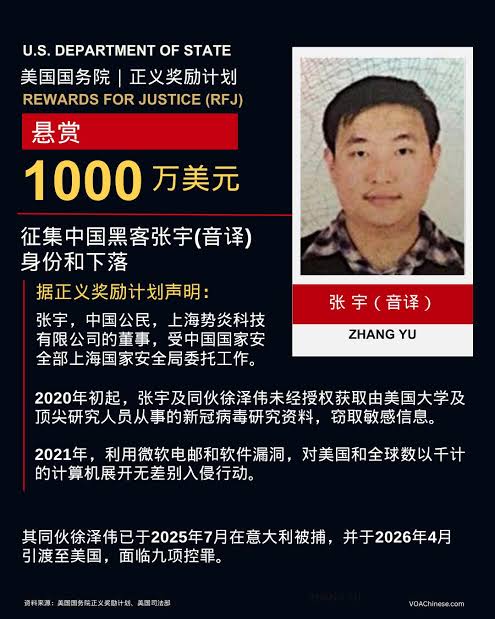
Rewards for Justice (RFJ) is offering a reward of up to $10 million for information
leading to the identification or location of any person who, while acting at the
direction or under the control of a foreign government, participates in malicious
cyber activities against U.S. critical infrastructure in violation of the Computer Fraud
and Abuse Act.
Under this reward offer, RFJ seeks information on Zhang Yu, a Chinese national and
director at Shanghai Firetech Information Science and Technology Company, Ltd.
working at the behest of the People’s Republic of China (PRC) Ministry of State
Security (MSS) Shanghai State Security Bureau (SSSB). The MSS and SSSB are PRC
intelligence services responsible for the country domestic counterintelligence, non-
military foreign intelligence, and aspects of the PRC’s political and domestic security.
Starting in early 2020, Zhang and his partner Xu Zewei, then a general manager at
Shanghai Powerock Network Co. Ltd., gained unauthorized access to COVID-19
research conducted by U.S.-based universities and leading immunologists and
virologists to steal sensitive information.
The following year, Zhang and Xu exploited vulnerabilities in computers running
Microsoft Exchange Server, a computer program involved in the storage and retrieval
of e-mails. Those intrusions were part of mass intrusion campaign, publicly known
as HAFNIUM, which compromised thousands of computers worldwide. Among the
victims were a university and a law firm, both based in the United States. Xu was
arrested by Italian law enforcement and extradited to the United States in April 2026.
Zhang remains at large.
The PRC uses an extensive network of private companies and contractors in China
to hack and steal information in a manner that obscures the PRC government’s
involvement.
“正义奖赏”(Rewards for Justice,简称 RFJ)计划悬赏最高 1000 万
美元,以征集有助于确认或定位相关人员身份及下落的信息;
该类人员须是在外国政府的指示或控制下,违反《计算机欺诈与
滥用法》(Computer Fraud and Abuse Act),参与针对美国关键基础
设施的恶意网络活动。
在此悬赏计划下,RFJ 寻求有关张宇(Zhang Yu)的信息。张宇是
中国公民,也是上海火泰信息科技有限公司(Shanghai Firetech
Information Science and Technology Company, Ltd.)的负责人,他
受中华人民共和国(PRC)国家安全部(MSS)上海市国家安全局
(SSSB)的指使开展活动。MSS 和 SSSB 属于中国的情報机构,
负责国内反间谍工作、非军事类境外情报工作,以及涉及政治与
国内安全的相关事务。
自 2020 年初起,张宇与其同伙徐泽伟(Xu Zewei,时任上海
博锐克网络科技有限公司总经理)未经授权访问了由美国高校及
顶尖免疫学家和病毒学家开展的 COVID-19 研究项目,企图窃取
敏感信息。
次年,张宇和徐泽伟利用了运行 Microsoft Exchange Server(一款
用于电子邮件存储与检索的计算机程序)的计算机系统漏洞。
这些入侵行动属于代号为“HAFNIUM”的大规模入侵行动的一部分,
该行动导致全球数千台计算机遭到入侵。受害者包括位于美国的
一所大学和一家律师事务所。徐泽伟于 2026 年 4 月被意大利执法
部门逮捕并引渡至美国,而张宇目前仍然在逃。
中国利用国内广泛的私营企业和承包商网络进行黑客攻击和信息
窃取,以此掩盖中国政府的参与。